Technical and scientific examinations of devices, systems and digital environments, with a documented chain of custody and internationally recognised methodology.
Wherever there is data, there is a trace; wherever there is a trace, an examination is possible. This practice covers the full spectrum of digital environments:
Desktops, laptops, servers, hard drives, SSDs and USB sticks: from system artefacts to deleted content.
Android and iOS: messages, apps, location, media and the link between the content and the device.
Go to the examination page →Authenticity, integrity and authorship of conversations: from the challenged screenshot to hash-verified extraction.
Go to the examination page →DVRs, IP cameras, trackers, vehicle infotainment systems, drones, smartwatches and connected devices: the evidence nobody remembers exists, and which proves decisive in accidents, employment cases and investigations.
Transactions, audit trails, connection logs and access records in corporate systems and infrastructure: who did what, and when.
Corporate e-mail, cloud storage and social platforms, with documented and lawful collection.
Each of the most requested examinations has its own page, setting out the method, the reach and the limitations, all stated before any engagement.
Logical, file system or physical extraction from smartphones and tablets (Android and iOS): messages, apps, location history, media with metadata, deleted content and the link between the content and the device, with hash values and sealed media.
See the examination →Authenticity, integrity and authorship of conversations: why a screenshot is not enough, what hash-verified extraction demonstrates and how fraud in screen captures is proven technically.
See the examination →Laptops, desktops, servers, hard drives, SSDs and USB sticks: bit-for-bit forensic imaging, analysis of system artefacts, a timeline of use and content recovery, with the original preserved and all work carried out on copies.
Scams, intrusions, misappropriation and online fraud: reconstruction of how the fraud unfolded, attribution of authorship and materialisation of the evidence for administrative or judicial accountability.
The origin, extent and destination of the breach: who accessed the data, when, how it left and where it went. The technical basis for incident response, regulatory notification and accountability.
When the device holding the evidence is damaged, formatted or wiped: an in-house laboratory that recovers the data and delivers, along with the files, the chain of custody that supports them.
See the examination →
The device used in the fact cannot always be examined. It may be an employee's personal mobile phone, a laptop that never belonged to the company, a machine that has already disappeared. But every access to the company's systems goes through its network, and the network keeps records.
Network forensics examines that path: packet capture and analysis, session reassembly, connection logs and the communication between the machines involved, from the identification of the device on the network to the application protocol. The examination answers who connected, from which device, to which systems, at what times and how much data went out. It also serves when the suspicion is of compromised machines talking to each other or to an external server.
Challenge. Confidential data was leaving the company on a recurring basis. Suspicion fell on an employee who accessed the systems from his own personal device, and the device, being his, could not be examined.
Method. The examination analysed the traffic on the company's network and proved the recurring exfiltration from that device.
Outcome. The network analysis grounded the injunction for search and seizure of the device, which was then examined under court order. The examination confirmed the presence of the confidential data and identified its transfer to a competing company.
Disputes between a company and a carrier, or between a call centre and its client, are almost always settled in the records. At stake are the call detail records (CDR), the carrier's invoices, the company's control systems and the service metrics. The examination cross-checks these sources and shows where they diverge and why.
The details that decide the case usually go unnoticed: an invoice in UTC compared with a system on Brasília time, or short calls excluded from the count. Another example is recording files automatically deleted under a card data security rule (short retention period). Each one changes the final figure, and the report shows the effect of each.
As the court-appointed expert, the examination established whether a company was breaching its contract with the carrier by using the contracted lines as VoIP traffic termination. The technical answer came out of the call records of the lines.
The invoice for a toll-free (0800) line showed more calls than the company's control system, in the ERP and the CRM, recorded. The examination cross-checked the two sources to separate the calls that actually took place from those that only appeared on the bill.
Whoever defrauds an ERP rarely uses the system's screen, which records who did what. He alters the data directly in the database, bypassing the application's rules, or issues invoices and documents the normal process would never generate. Alteration from outside leaves marks: a record without the corresponding event in the audit trail, a broken sequence, inconsistent dates between tables, traces in the database itself. The examination gathers those marks and shows what was altered, when and, if the records allow, by which account.
The files extracted from a drone hold the take-off location, the route of the last flight and the usage history of the device. In examinations already carried out, those records showed where the equipment departed from and the path it took. It is useful evidence in accidents, trespass, unlawful image capture and disputes over the use of the equipment.
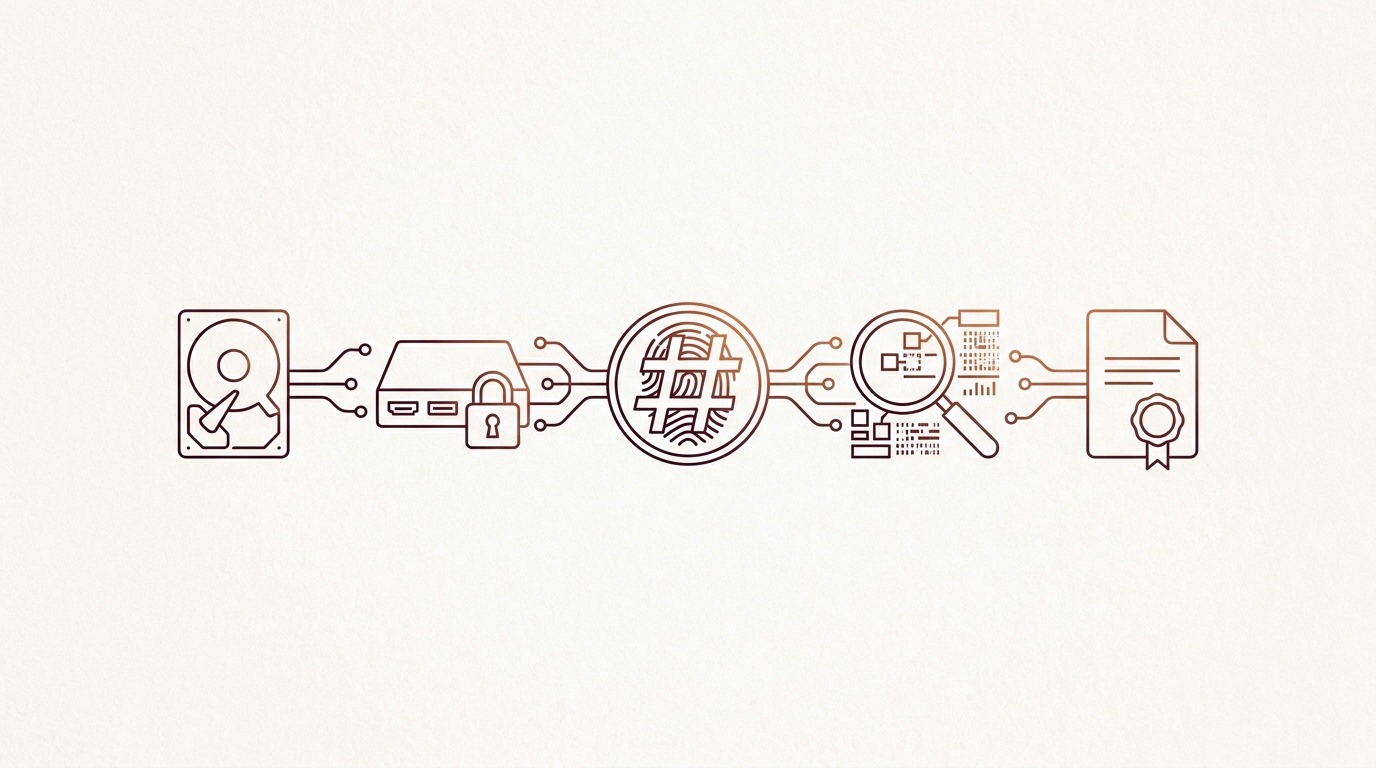
Every examination in this practice goes through the same five stages, aligned with ABNT NBR ISO/IEC 27037 and documented from first contact to delivery:
The normative basis is named, not decorative: ABNT NBR ISO/IEC 27037 for identification, collection and preservation; NIST SP 800-86 and 800-101 for the forensic process and for mobile devices; RFC 3227 for the order of volatility; and CPP, arts. 158-A to 158-F (Brazilian Code of Criminal Procedure) for the chain of custody. Every report records what was done, with what, and under which criteria, so that the method can be repeated and checked.

Digital forensics cannot be improvised on an ordinary laptop. Examinations take place in a dedicated laboratory, with forensic-grade equipment:
Collection and preservation in accordance with ISO/IEC 27037: the original media is read without a single bit being written to it, using hardware write blockers and forensic duplicators that generate the bit-for-bit image in a forensic container, with the hash calculated during the acquisition itself. Duplication is carried out on internationally recognised equipment, capable of processing up to 7 NVMe and 4 SATA/SAS source drives simultaneously, with output to 2 SATA/SAS and 2 NVMe drives. Every forensic examination is performed solely on the copy, known as the forensic image.
Mobile device extraction carried out by someone with deep knowledge of how complex this type of analysis is: Adriano Vallim served as a Cellebrite instructor for Latin America, training the law enforcement teams that operate the tool. That same experience serves both to perform extractions and to review, technically, extractions carried out by third parties.
Analysis servers separate from the acquisition workstations, able to index and correlate large volumes: in cases involving multiple devices or bulky data, the data is correlated to reveal links and to identify every trace.
After collection and forensic indexing, the media holding the preserved data waits in a secure vault room compliant with ABNT NBR 15247 / EN 1047-2 until the case is closed, with restricted access and continuous monitoring.
Digital evidence does not end with the report. It must be born preserved, live in custody and, when the case closes, be destroyed securely. Few experts look after the entire cycle; here, it is part of the method.
Write blockers, bit-for-bit forensic imaging performed with hardware used by law enforcement worldwide, hash values calculated at collection and checked at verification. The original is sealed and stored in a secure vault room; every examination takes place on faithful copies.
Media held in custody is stored in a vault room certified to industry standards (ABNT NBR 15247 / EN 1047-2): protection against fire, water, gases and electromagnetic fields, controlled climate, restricted access and continuous monitoring. The evidence waits out the proceedings under bank-grade security.
Almost no expert offers it, and every company needs it: certified forensic sanitisation of media and devices, using recognised methods and issuing a certificate of destruction. Data that must cease to exist ceases to exist provably, in compliance with the Brazilian data protection act (LGPD).

Technical honesty is part of the method. Before any engagement, it is worth knowing that:
Analysis of a mobile device with recovery of app data, timeline reconstruction and a report of more than 300 pages delivered in 45 days.
Appearances on Jornal da Record and Band explaining the technical process of forensic extraction to the public.
Challenge. The third-placed bidder in a public tender went to court to annul it, alleging fraud, and presented digital material as evidence.
Method. Examination of the material and of the metadata of the file presented.
Outcome. The evidence had been produced in a tampered browser, and the metadata of the forged material pointed to who created it. The claim seeking to annul the tender failed, and the winning bidder was able to provide the services.
See also
Forensic Extraction from Mobile Phones → WhatsApp and Conversation Examination → Forensic Data Recovery → Digital Questioned Document Examination → Expert Reports and Opinions →
Before deciding, it is worth seeing what has already come through this laboratory: cases described without identifying the parties, in the format of challenge, method and result.
The intruder's control channel was written into smart contracts. The examination decoded what he had deleted and handed the authorities concrete routes to identification.
See the case Negative proofThe official examination had concluded that he took part. The re-examination showed the links were false positives, and the accused person was cleared.
See the case